@jw thanks for additional insight!
Unfortunately we simply won't have the opportunity to explore this until well past ProGet 2024, and only after we've gotten sufficient feedback from other early adopters on other gaps. I think there are other important things we need to consider as well, and handlign this is so much more complicated to handle this than it may seem, especially at scale and with how our ProGet is configured in the field.
There are also other mechanisms like policy exceptions built-in that could easily handle System.* and runtime.* packages, as I suspect the only thing you would worry about those are vulnerabilities.
As an alternative, I would if you could just write a tool/script to:
- query for inconclusive builds
- download inconclusive/missing package builds through a feed
- trigger a reanalysis of the build
That's not optimal, but that is one thousand times easier than getting something liket his working in PRoGet.

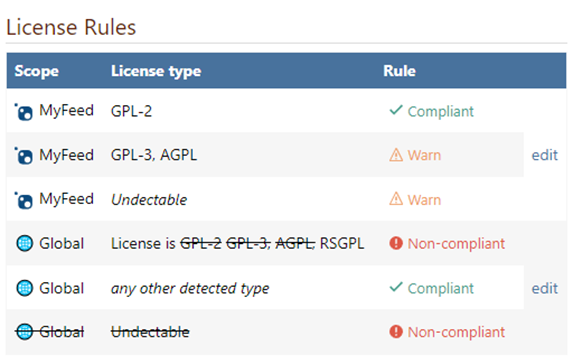
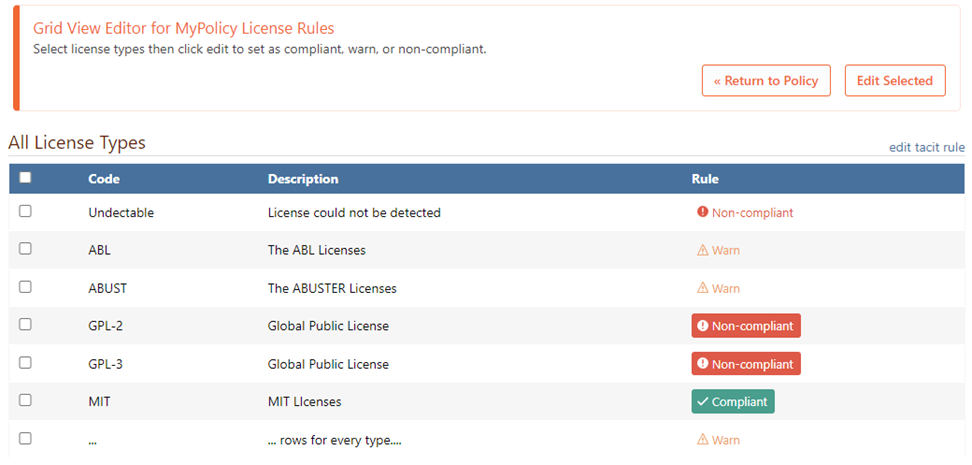


 security tool

 ). I've put a note onto our roadmap planning board, and may jump back or email you directly for some feedbakc/insight