Welcome to the Inedo Forums! Check out the Forums Guide for help getting started.

If you are experiencing any issues with the forum software, please visit the Contact Form on our website and let us know!

  • 0 Votes
    3 Posts
    15 Views
    O
    Hi @stevedennis, Thank you very much for your answer. From what I've read elsewhere, that's exactly what I thought. By the way, and besides that, ProGet is a really great tool. Good job ! Regards, Olivier
  • ProGet: Strategies for (more) flexible feed naming

    Support
    3
    0 Votes
    3 Posts
    11 Views
    G
    Thanks for the tips. That Docker constraint is particularly good to know, I hadn't realized! We do have a rather large amount of feeds to manage, including a (growing) set of feeds we use as local mirrors. I'll see if we can find an alternative solution that works for us...
  • Install Issues - Docker Compose + Postgres

    Support
    8
    1 Votes
    8 Posts
    26 Views
    stevedennisS
    Hi @jeremy-oaks_9309 , Just wanted to respond to this real quick: I have ~80k packages (~600GB) -- so we're opting for the stand-alone database for performance purposes Based on this information we still recommend using the embedded database; it's almost always going to be more performant as well as simpler to maintain. 80k is not that many packages by any stretch. While @pg_user_8607 is correct in that it's a bit easier to monitor database performance, investigate issues like bad queries, and do DBA maintenance tasks - that's all technically "our job". From a user perspective, the only required "database maintenance" should be backing up the files. We certainly don't mind the help (and users like @pg_user_8607 have helped us out a lot!!), and it may be quicker if you "know what you're doing" to get to a root issue, since we're not all exactly experts at all these layers. But I just wanted to make sure you were aware of the pros-and-cons. Thanks, Steve
  • 0 Votes
    2 Posts
    7 Views
    stevedennisS
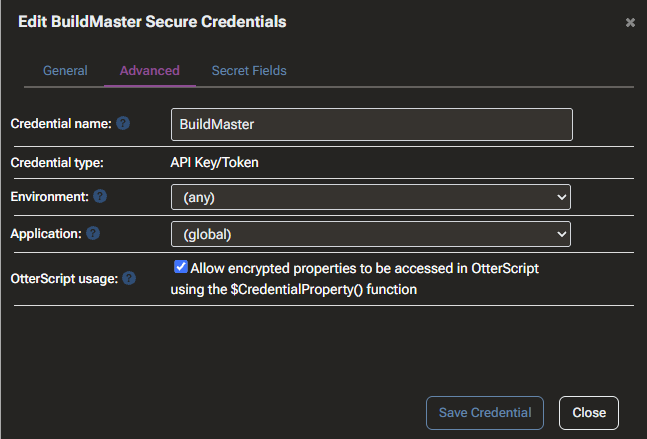
    Hi @brandon_owensby_2976, I wasn't able to reproduce this issue, but looking over the code, I can see a few scenarios in which "not configured to allow access to encrypted values" will trigger, even if that's not accurate. It's not trivial to rewrite that to provide a more accurate error message or credential resolution, so we'll add this to our BuildMAter 2027t roadmap and review it more closely then. In the meantime, I would just use a variable and duplicate the information. Thanks, Steve
  • 0 Votes
    6 Posts
    17 Views
    gdivisG
    Glad I could help! We'll get that documentation updated as well.
  • 0 Votes
    9 Posts
    33 Views
    stevedennisS
    Hi @brandon_owensby_2976 , You can configure release settings on an application-by-application basis under the Settings tab. In this case, you'd set Release Usage to be Optional or Disabled. If Release Usage is set to Required, users must select a release when creating a new build; this was the deefault in older versions of BuildMaster. https://docs.inedo.com/docs/buildmaster/modeling-your-applications/buildmaster-releases Cheers, Steve
  • 0 Votes
    4 Posts
    13 Views
    apxltdA
    Hi @fabrice-mejean , Thanks so much for the detailed information and offer to connect further! Very interested in that and I will definitely take you up on that :) Please give me a little time for that; I've got some travel coming up and then a bunch of other things... so I'd like to connect when I can really focus on some of these future things. . Cheers, Alex
  • 0 Votes
    8 Posts
    87 Views
    stevedennisS
    @Nils-Nilsson excellent, let us know as you have other feedback too! This is definitely an area we intend to keep improving in throughout ProGet 2026+
  • 0 Votes
    4 Posts
    19 Views
    stevedennisS
    Hi @carl-westman_8110 , Thanks for sharing that. This isn't a symptom of "server overload" that we've seen before. The error you shared is occurring on Feeds_GetFeeds, which is definitely not an intensive query, and I would not expect that to be timing out at all. It's just SELECT * FROM [Feeds]. However, that's a similar symptom to the "AzureSQL resource throttling" that we've seen on other users: another query is being throttled (for example, something that joins on [Feeds]), and that is causing a cascading impact on other queries. We don't have enough information to say that's the case here. But, an easy way to test would be to up your DTUs substantially. Otherwise, the next troubleshooting step is to try to identify the cause of the timeouts, which involves looking at HTTP Access logs and jobs occurring around the same time under Admin > Scheduled Jobs. Thanks, Steve
  • API request to get latest image or chart?

    Support
    2
    0 Votes
    2 Posts
    10 Views
    atrippA
    Hi @jeff-miles_5073 , You can get information about images and tags using the Docker API; we do not provide documentation on how to use that (see our caveat on Feed Endpoints). And unfortunately the Docker API is a bit awkward, but with enough ChatGPT you should be able to figure it out :) You could also query the database directly, perhaps building some kind of data export tool so that you can sync it with your dashboard. Hope that helps, Alana
  • 0 Votes
    4 Posts
    24 Views
    rhessingerR
    Hi @joris-guex, Thanks for sending an example over. It looks like this is related to an issue in the libssh2-sys's manifest. I have created a ticket, PG-3321, to handle these issues better. We are expecting to have a fix out within the couple of maintenance releases of ProGet 2026. Thanks, Rich
  • ProGet pnpm audit reports no vulnerabilities

    Support
    4
    0 Votes
    4 Posts
    29 Views
    stevedennisS
    Hi @Ashley , Amazing, thanks for this investigation! This is very helpful. You've also captured the exact issue we have with a lot of these APIs; no real specs (or worse... wrong specs), which involves a reverse engineering effort. This quote is wonderful: In summary, due to the lack of an official JSON schema and potential changes between npm versions, it's crucial to treat the npm audit --json output structure as subject to change. Relying solely on the npm CLI source code for the most accurate and up-to-date information is recommended, along with implementing robust version checks and testing in your development processes. Wouldn't it be nice if we could build our products like that! Anyway, I was curious and I asked internally, and the original engineer is almost certain that npmjs used to have the CVE number there, which we also used to emit until changing to PGVD number in ProGet 2023. But that is consistent with their position of "we don't do specs, just read the latest commit to figure it out. But it doesn't really matter, that's what we have now... To ensure consistency with the public npm registry, would it be possible to change ProGet to use a number for the id field on the audit response? If you discovered this in ProGet 2025, we'd just change it in ProGet 2026 and not worry about it. But we need to be super-careful making API changes in a maintenance release. We can't quite get away with Microsoft/GitHub levels of quality :) Seemingly harmless changes lead to broken builds, which are really painful to debug; for example, we recently added upload-time to PyPI API. That caused older versions of the pip client to break due to a bug in how they parsed dates. There are probably too many client/versions to answer the question "what is this field even used for and what are the consequences of changing it?" Perhaps an easier route is to just get pnmp to change to a string, like the rest of them? Or, just ignore it and "let it be"? Over time, if you follow our recommend best practices, these audits will show fewer and fewer vulnerabilities. We plan to continuously refine the PVRS algorithm to better combat both "vulnslop" (i.e. AI-discovered and AI-generated vulnerabilities that cannot be exploited in any real-world scenario nor would cause any real-world harm if so) and misreporting. Thanks, Steve
  • Block recently published - Metadata filter ?

    Support
    4
    1 Votes
    4 Posts
    28 Views
    apxltdA
    @jens-viebig_4541 ooh good catch! That guidance is outdated as of ProGet 2026, where we no longer recommend/default to blocking Noncompliant packages. We should rewrite/republish the article to be more focused on guidance, update the screenshots, etc. I'll add that to the list.
  • 0 Votes
    2 Posts
    7 Views
    stevedennisS
    Hi @svc-4x9p2a_6341 , This is known issue and will be addressed via PG-3309 in the next maintenance release. You can just ignore the messages for the time being, it only happens like once a week or so.... I wouldn't modify the database either. Thanks, Steve
  • 0 Votes
    4 Posts
    15 Views
    stevedennisS
    Hi @mhelp_5176, Connecting to the embedded database requires local access to the ProGet server. Once an attacker has that, then they already have full access to the database, as it's stored as files on disk... basically it's the equivalent of storing the safe key inside of the safe :) As such. it doesn't make sense for us to add complexity to the product to support changing a password that's already secured. Thanks, Steve
  • User gets 500 error if you delete a logged in user

    Locked Support
    4
    0 Votes
    4 Posts
    16 Views
    stevedennisS
    Hello, Thanks for reporting this; this behavior is by design. ProGet uses authentication tickets (i.e. encrypted cookies). If the username on a valid ticket cannot be located in the user directory, then a "user not found" error will occur, as it did here. This errant behavior is generally desired for troubleshooting cases where users are intermittently not available from a user directory. Otherwise it's very difficult to troubleshoot, since it will just appear as a random log-out. Thanks, Steve
  • PostgreSQL DB Location

    Support
    5
    0 Votes
    5 Posts
    27 Views
    atrippA
    Hi @mhelp_5176, Not at this time; this would add complexity to the software and installation, so we're hesitant to give an option to configure this path without a compelling technical benefit. Given your requirements, perhaps they should just configure the %ProgramData% folder to be on a different drive? Many Windows programs use that location for data like this. Or perhaps configure a junction (soft link). Thanks, Alana
  • Add Documentation for Chocolatey Proxy feeds

    Support
    11
    0 Votes
    11 Posts
    34 Views
    apxltdA
    Hi @imm0rtalsupp0rt , We've published a version of the article now: https://docs.inedo.com/docs/proget/feeds/chocolatey/howto-chocolatey-proxyccr Let us know your thoughts or freel free to submit a PR should have have any suggestions! Thanks, Alex
  • 1 Votes
    6 Posts
    20 Views
    stevedennisS
    @sigurd-hansen_7559 wow very cool! We didn't anticipate anyone would customize these templates beyond adding a variable or two, so it it didn't seem to make a lot of sense to invest in a proper editor (like we have in the other products) Anyway, it'd be interesting to see what kind of templates you develop.
  • Support for Azure Key Vault references in Connector credentials

    Support
    2
    0 Votes
    2 Posts
    4 Views
    stevedennisS
    Hi @alkhleif_2585 , There isn't much demand for this kind of feature (I think we've only seen one or two requests for this over very many years) so it's not on our roadmap. And it's unlikely we will add it to the roadmap considering that it would be quite costly to build, support, and maintain. Especially considering that we'd need to support all of the major "vaults" out there as well. It doesn't seem to add much value to ProGet as these types of read-only credentials can be very long living (several years) without any security risk, and take just a few minutes to rotate when needed. That being said, you could probably write a "sync script" pretty easily that continuously updates the connector credentials by connecting to the vault and then updating it via the API. Cheers, Steve